

ISC CISSP-German exam dumps : Certified Information Systems Security Professional (CISSP Deutsch Version)
- Exam Code: CISSP-German
- Exam Name: Certified Information Systems Security Professional (CISSP Deutsch Version)
- Updated: Oct 14, 2026 Q & A: 1811 Questions and Answers

 PDF Version Demo

PC Test Engine
ISC CISSP Deutsch Value Pack (Frequently Bought Together)

- If you purchase ISC CISSP Deutsch Value Pack, you will also own the free online test engine.
- PDF Version + PC Test Engine + Online Test Engine
- Value Pack Total: $139.98 $89.99
About ISC CISSP Deutsch Exam
Your next certification deserves a discount: PracticeTorrent rewards returning CISSP Deutsch customers with bountiful savings on future purchases, because one pass with the ISC Certified Information Systems Security Professional (CISSP Deutsch Version) material is rarely the last.
ISC CISSP Deutsch Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Communication and Network Security | 13% | - Implement secure design principles in networks
|
| Identity and Access Management | 13% | - Integrate identity as a service
|
| Software Development Security | 11% | - Understand software development lifecycle security
|
| Security Operations | 13% | - Conduct logging and monitoring activities
|
| Security and Risk Management | 15% | - Understand legal and regulatory issues
|
| Asset Security | 10% | - Identify and classify information and assets
|
| Security Architecture and Engineering | 13% | - Select controls based on security requirements
|
| Security Assessment and Testing | 12% | - Conduct security control testing
|
CISSP Deutsch Exam FAQ: Pooling Efforts With ISC Candidates
ISC Certified Information Systems Security Professional (CISSP Deutsch Version) is an official ISC2 certification exam, registered under the code CISSP Deutsch. Passing it awards the ISC Certification certification, a credential at the Expert level. It also connects to ISC2 Certified Cloud Security Professional (CCSP), ISC2 Systems Security Certified Practitioner (SSCP), ISC2 Certified in Cybersecurity (CC). Successfully passing matters to every candidate because the credential keeps working for your career long after exam day.
You will answer 100-150 questions within 180 minutes on the ISC Certified Information Systems Security Professional (CISSP Deutsch Version) exam. That combination rewards candidates who practiced under realistic timing, so make timed sessions in the PracticeTorrent engine a daily habit; one to two hours a day is enough when every minute rehearses the real thing.
ISC Certified Information Systems Security Professional (CISSP Deutsch Version) requires 700 out of 1000 to pass, and official registration costs USD $749. Since every retake charges USD $749 again, diligent daily practice is the cheapest strategy available. Let your PracticeTorrent practice scores confirm readiness across several consecutive sessions before you book.
Minimum 5 years cumulative paid work experience in two or more CISSP domains. A relevant four-year degree or approved credential may substitute for one year of experience.
Vendor requirements do change, so verify the current conditions before registering on the official exam page.
The ISC Certified Information Systems Security Professional (CISSP Deutsch Version) blueprint covers 8 domains, with the largest being Security Architecture and Engineering (13%), Identity and Access Management (13%), and Security Assessment and Testing (12%). The full topic list is above on this page; it tells you exactly where your daily hour or two earns the most marks.
Yes, download the free demo of the ISC Certified Information Systems Security Professional (CISSP Deutsch Version) questions before deciding, and read former customers' comments for an independent verdict. After purchase, new versions download free for one year, and when your product expires you can extend the update service at a 50% discount. Returning customers also enjoy bountiful discounts on future exams.
Your purchase carries a 100% money-back guarantee with defined conditions. Take the ISC Certified Information Systems Security Professional (CISSP Deutsch Version) exam within 60 days of purchase; if you fail, you may claim a full refund, provided the exam matches your product. Attempts within 3 days of purchase are ineligible, as are downloaded-but-unused products, free materials, and expired orders; the candidate name must match the payer name. Submit a scanned enrollment slip and the official Score Report PDF within 2 days of the exam, and claims are processed within 7 days. Alternatively, exchange for two other exam products of equal value, free, with your original purchase keeping its update service.
Delivery is instant: download upon payment, with an email copy arriving within one minute. If nothing arrives within 2 hours, check spam and contact our 24/7 agents, who solve problems with infinite patience. Installation is unlimited across your computers.
ISC Certified Information Systems Security Professional (CISSP Deutsch Version) Sample Questions:
Welche der folgenden Aussagen beschreibt „Shoulder Surfing“ am besten?
- A. Ausnutzen einer Software-Schwachstelle zum Erlangen unberechtigten Zugriffs
- B. Abfangen des Netzwerkverkehrs in einem gemeinsam genutzten drahtlosen Netzwerk
- C. Das Ausspähen vertraulicher Informationen einer Person, wie z. B. eines Passworts, durch Über-die-Schulter-Schauen.
- D. Verwendung eines gestohlenen Zugangsausweises zum Betreten einer Einrichtung
Correct Answer: C 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
Ein Sicherheitstechniker wird mit der Gruppe für das Patch- und Schwachstellenmanagement beauftragt. Die Bereitstellung eines neuen Patches wurde genehmigt und muss angewendet werden.
Die Recherche ist abgeschlossen und der Sicherheitstechniker hat Empfehlungen abgegeben. Wo sollte der Patch ZUERST angewendet werden?
- A. Serverumgebung
- B. Desktop-Umgebung
- C. Produktionsumgebung
- D. Untere Umgebung
Correct Answer: D 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
Welche der folgenden Ergebnisse würden MOST wahrscheinlich auf ein hohes Risiko in einem Schwachstellenbewertungsbericht hinweisen?
- A. TCP-Port 443 (Transmission Control Protocol) geöffnet
- B. Nicht standardmäßige Systembenennungskonvention verwendet
- C. End-of-Life-System erkannt
- D. Nicht lizenzierte Software installiert
Correct Answer: C 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
Bei der Entwicklung eines nach außen gerichteten webbasierten Systems, welcher der folgenden Punkte wäre der HAUPT-Fokus der Sicherheitsbewertung vor der Implementierung und Produktion?
- A. Sicherstellen, dass die Eingabevalidierung erzwungen wird
- B. Sicherstellen, dass SSL-Zertifikate (Secure Sockets Layer) intern signiert sind
- C. Sicherstellen, dass SSL-Zertifikate (Secure Sockets Layer) von einer Zertifizierungsstelle signiert werden
- D. Bewertung des Uniform Resource Locator (URL)
Correct Answer: A 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
Was ist das Recovery Point Objective (RPO) bei der Wiederherstellung nach einem Ausfall in Bezug auf die Datenwiederherstellung?
- A. Das RPO ist die Zeit, die benötigt wird, um einen akzeptablen Prozentsatz verlorener Daten wiederherzustellen.
- B. Das RPO ist ein Ziel, um einen bestimmten Prozentsatz verlorener Daten wiederherzustellen.
- C. Das RPO ist die minimale Datenmenge, die wiederhergestellt werden muss.
- D. Das RPO ist die maximale Zeitspanne, für die ein Datenverlust akzeptabel ist.
Correct Answer: D 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
Viewing page 1 out of 363 pages.
Viewing questions 1-5 out of 1811 questions.


Related Exams
Related Certifications
Over 75621+ Satisfied Customers
Popular Vendors
What Clients Say About Us
Why Choose Us
-
QUALITY AND VALUE
PracticeTorrent Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
-
TESTED AND APPROVED
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
-
EASY TO PASS
If you prepare for the exams using our PracticeTorrent testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
-
TRY BEFORE BUY
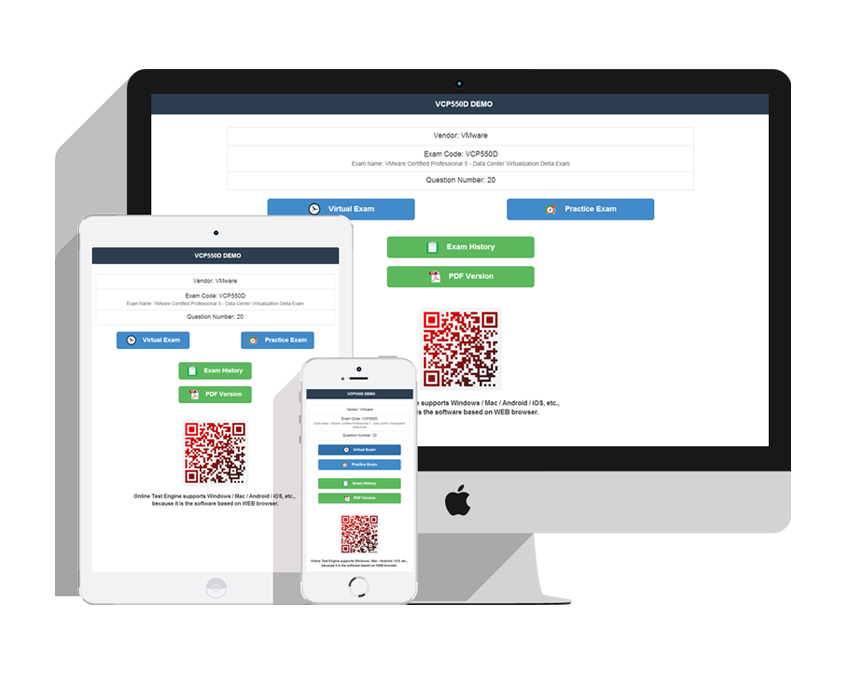
PracticeTorrent offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
Our Clients





Get the high score and achieve the certification with our latest practice torrent. The complete exam prep torrent contains the questions & answers which are related to the actual test. You can pass your actual test at first attempt.
Tags
- Databricks-Certified-Data-Engineer-Associate practice torrentMay 28, 2022
- CAD-JPN practice torrentMay 28, 2022
- Sales-Admn-202 practice torrentMay 28, 2022
- CISA-CN practice torrentMay 28, 2022
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 PracticeTorrent NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy